Managed SOC Services (24/7 Security Operations)
CloudAct’s Managed SOC delivers round-the-clock monitoring, threat detection, incident response, and continuous security analytics to keep your organization protected from evolving cyber threats.
Request SOC Assessment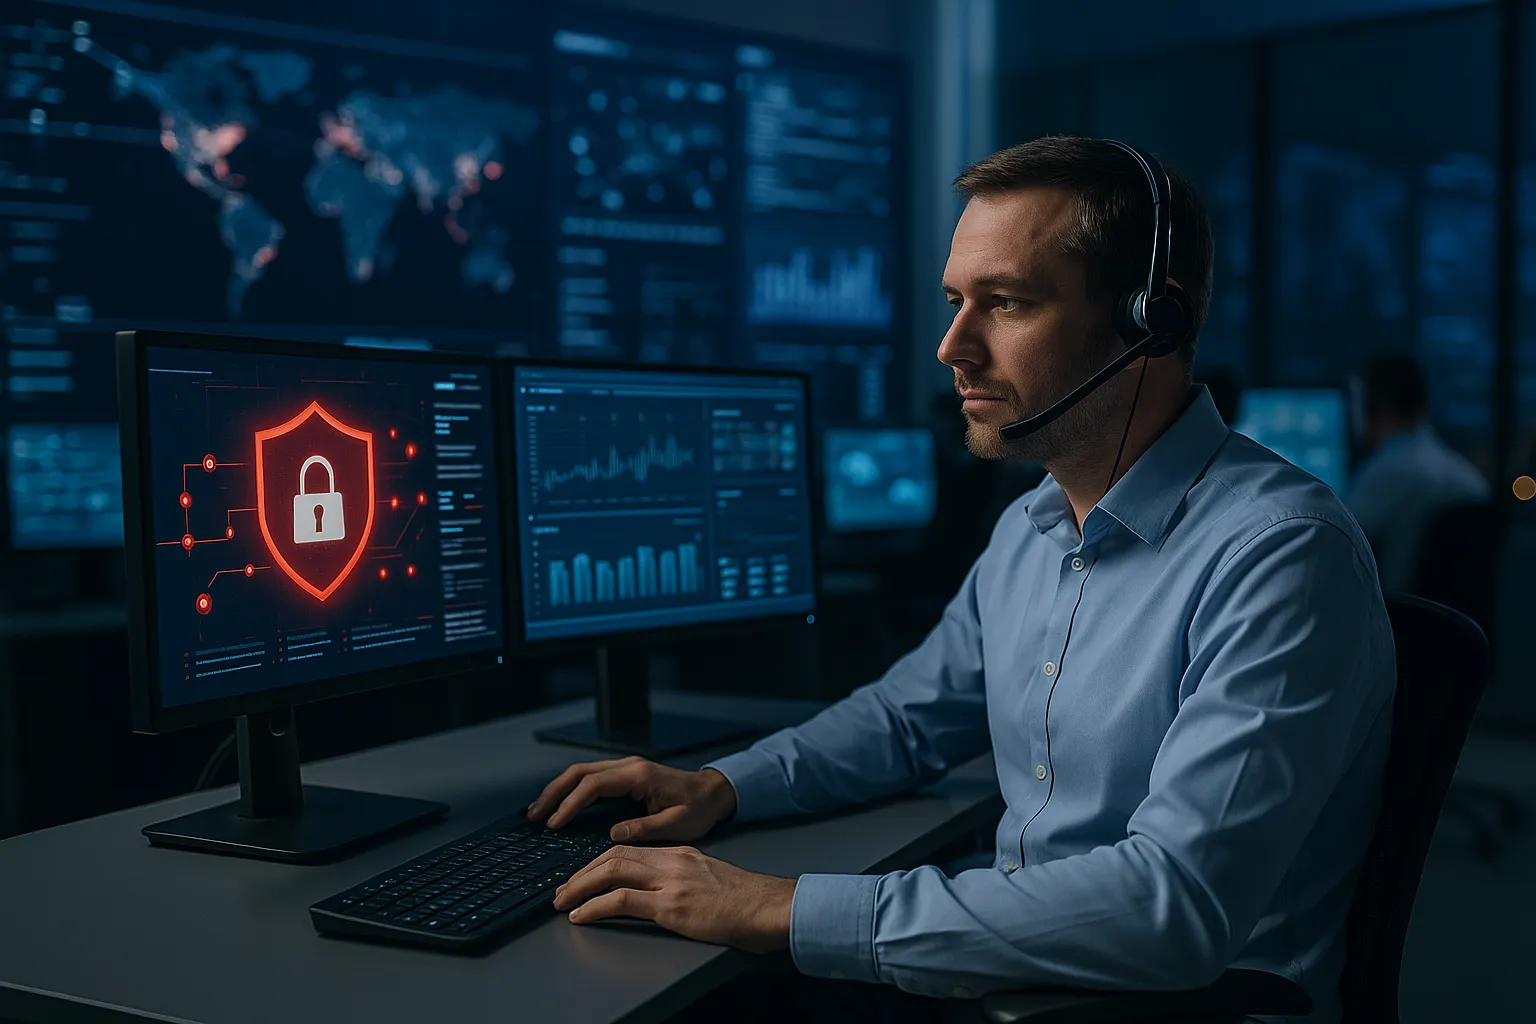
24/7 Security Monitoring. Rapid Detection. Effective Response.
Cyber threats are more advanced and persistent than ever. Organizations require continuous monitoring and specialized expertise to detect and respond to threats before they cause damage.
CloudAct’s Managed SOC provides real-time threat detection, SIEM correlation, incident handling, and continuous security analytics backed by certified SOC analysts and advanced security tools.
Core Functions of Our Managed SOC
24/7 Threat Monitoring & Alerting
SIEM Log Collection & Correlation
Endpoint Detection & Response (EDR/XDR)
Real-time Incident Response & Containment
Threat Intelligence & IOC Enrichment
Vulnerability Monitoring & Prioritization
Security Device Management (Firewall, IDS/IPS)
Compliance & Security Reporting
Platform Capabilities & Security Features
Advanced SIEM with automated correlation rules
AI-driven anomaly detection & behavioral analytics
Threat blocking with SOAR orchestration
Continuous vulnerability scanning
Zero-Trust enforcement across endpoints & identities
Cloud workload protection (AWS, Azure, GCP)
Ransomware early-warning detection
Encrypted log storage & compliance retention
Powered by globally recognized SOC & SIEM technologies
Threat Detection Coverage
Malware & Ransomware
Insider Threats & Privilege Misuse
Cloud Misconfigurations
Network Intrusions & Lateral Movement
Compromised Credentials
Zero-Day Exploits Behavior
Phishing Campaigns & Email Threats
Suspicious API & Application Activity
Our SOC Workflow
1. Log & Telemetry Collection
Aggregate logs from endpoints, networks, cloud, and applications.
2. Correlation & Threat Detection
SIEM and XDR engines analyze events in real-time.
3. Alert Triage & Investigation
SOC analysts validate alerts, filter noise, and prioritize threats.
4. Incident Response
Contain threats through isolation, blocking, or credential resets.
5. Forensics & Reporting
Provide root cause analysis, timelines, and recovery recommendations.
Industries Protected by Our SOC
Financial Services
Government & Defense
Healthcare & Hospitals
Manufacturing & Industrial
Telecommunications
Retail & E-commerce
Education & Research
Strengthen Your Defense with Managed SOC
CloudAct provides 24/7 monitoring, rapid incident response, and deep threat visibility across your entire IT environment.
Talk to a Cybersecurity Specialist